Reported Bluetooth Flaw Puts 16 DJI Drone Models Under Review
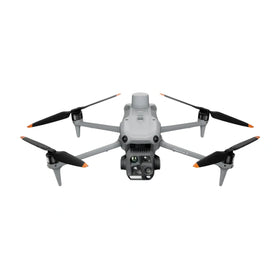
A newly reported Bluetooth vulnerability has drawn attention to 16 DJI drone models, raising fresh questions about fleet security, firmware patching, and how commercial operators should approach the pre-owned DJI market while details remain limited.

Quick answer
A reported Bluetooth flaw has placed 16 DJI drone models under scrutiny, according to a DIY Photography report, though technical specifics and official confirmations remain limited.
- The report names 16 DJI drone models as potentially affected by a Bluetooth-related vulnerability
- No official DJI confirmation or firmware patch details are available in the source data
- Commercial operators should monitor firmware updates and assess fleet exposure
- Pre-owned DJI buyers may want to verify firmware status before purchase
A reported Bluetooth vulnerability has placed 16 DJI drone models under fresh scrutiny, according to a report published by DIY Photography and surfaced through Google News DJI. The report, which remains the primary source for this development, suggests that a flaw in Bluetooth implementation could have security implications for affected aircraft, though the technical specifics, severity ratings, and any official DJI response have not yet been detailed in the available reporting.
Operator checklist
Turn policy news into a safer fleet decision.
Before changing aircraft, compare repair paths, available DJI inventory, and trade-in timing against the rule change.

For commercial operators, fleet managers, and repair customers, the report matters less for what it definitively proves and more for what it signals: another reminder that connectivity layers on modern drones are now part of the security surface that procurement teams, maintenance planners, and second-hand buyers must evaluate. The absence of confirmed technical details does not eliminate the operational question. It sharpens it.
What the DIY Photography report actually says
The DIY Photography report is the named primary reporting source for this development. It identifies 16 DJI drone models as being implicated in a reported Bluetooth flaw, though the published summary available for this analysis does not list the specific model names, firmware versions, or vulnerability identifiers. Reboot Hub analysis cannot confirm which aircraft are affected, whether the flaw requires physical proximity to exploit, or whether DJI has issued a patch or advisory.
What the report does establish is that Bluetooth connectivity, a feature present across many consumer and enterprise DJI platforms, is being examined as a potential attack surface. For commercial readers, the practical takeaway is not to assume a specific drone is compromised. It is to recognize that wireless interfaces beyond the primary control link now sit inside the risk model for fleet operations, data handling, and asset resale.
The source-limited nature of this reporting means operators should treat the development as an early signal rather than a confirmed operational emergency. No agency, regulatory body, or DJI official statement is cited in the available source data confirming the flaw, its exploitability, or remediation status.
Why Bluetooth exposure changes fleet risk conversations
Bluetooth is often treated as a convenience layer: pairing a controller, syncing media, or connecting accessories. But in fleet environments, every wireless interface is a potential entry point. A reported flaw in Bluetooth implementation raises questions about whether an attacker could disrupt pairing, intercept telemetry, or interfere with pre-flight processes. None of those outcomes are confirmed in the source data, but the mere possibility shifts how procurement and maintenance teams think about firmware hygiene.
For operators running mixed fleets, the immediate step is inventory awareness. Knowing which aircraft are in service, which firmware versions they carry, and whether Bluetooth is enabled during mission profiles is baseline work that becomes more urgent when a vulnerability report circulates. Even without confirmed exploit details, a fleet manager can reduce exposure by disabling unused wireless features where operational needs allow and by tracking DJI's official channels for any advisory or patch release.
Repair providers face a related question. Customers bringing in affected models may ask whether a hardware repair, firmware update, or inspection changes the security posture of their aircraft. Without official confirmation of the flaw's nature, repair shops should avoid making security claims and instead focus on documenting firmware status and recommending that customers monitor manufacturer communications.
What this means for drone owners and the market
The pre-owned DJI market is sensitive to vulnerability reports, even when details are thin. Buyers evaluating a used aircraft often focus on physical condition, flight hours, and battery health. A reported Bluetooth flaw adds a fourth dimension: firmware and security status. A pre-owned drone that has not been updated to a patched firmware version, if and when DJI releases one, could carry residual risk that a buyer does not discover until after purchase.
This is where the commercial bridge becomes concrete. Operators and buyers who want to understand how a specific DJI model fits into repair, parts availability, and long-term ownership can consult the Drone Wiki for model-level context before making a purchase or service decision. The point is not to treat the reported flaw as a reason to avoid the pre-owned market. It is to treat firmware verification as a standard part of the used-drone inspection checklist, alongside physical wear and component condition. For owners evaluating service and lifecycle risk, Drone Wiki explains the relevant repair, parts, resale, or operational path.
For sellers, the report creates a documentation incentive. A pre-owned listing that includes current firmware status, update history, and confirmation that the aircraft has been checked against known advisories is more defensible in a market where buyers are becoming security-aware. Sellers who cannot answer those questions may face harder negotiations or slower sales.
The broader market implication is that connectivity-related vulnerabilities, whether confirmed or merely reported, compress the window during which operators can ignore software as a fleet management variable. Drones are no longer just airframes and cameras. They are networked devices, and the second-hand market will increasingly price that reality into transactions.
What operators should do while details remain limited
The responsible near-term response is measured, not reactive. First, operators should identify whether any of the 16 models named in the DIY Photography report are present in their fleet. Second, they should document current firmware versions and Bluetooth usage patterns for those aircraft. Third, they should monitor DJI's official support and security channels for any advisory, patch, or clarification. None of these steps require assuming the worst; all of them improve readiness if the report matures into a confirmed vulnerability with a defined remediation path.
Repair customers should ask their service provider to note firmware status on any work order, particularly for models that may be affected. This creates a paper trail that supports resale, insurance documentation, and internal compliance reviews. Fleet managers should also consider whether Bluetooth is necessary for their missions. If it is not, disabling the interface reduces the attack surface regardless of whether the reported flaw is ever confirmed.
Buyers in the pre-owned DJI market should add one question to their standard seller checklist: what firmware is installed, and has the aircraft been updated since the most recent security advisory cycle? A seller who cannot answer that question is not necessarily hiding anything, but the buyer now has a legitimate reason to ask.
FAQ
Frequently asked questions
Which DJI models are affected by the reported Bluetooth flaw?
The DIY Photography report names 16 DJI drone models, but the available source summary does not list the specific model names. Operators should check the original report and DJI's official channels for the full model list and any update.
Has DJI confirmed the Bluetooth vulnerability?
No official DJI confirmation is present in the source data. The development is based on a DIY Photography report, and operators should treat it as an unconfirmed signal until DJI or a regulatory body issues a formal statement.
Should I avoid buying a pre-owned DJI drone because of this report?
Not necessarily. The report does not confirm exploitability or real-world impact. A more measured approach is to verify firmware status, ask sellers about update history, and monitor official advisories before completing a pre-owned purchase.
Which sources support this update?
The article distinguishes reported information from analysis and does not present an unverified source as official confirmation.
What remains subject to change?
Retail pricing, availability, product bundles and regulatory timelines can change. Readers should verify the latest terms with the named retailer, manufacturer or regulator before acting.
How should buyers or operators use this analysis?
Use the verified facts as a starting point, then compare mission fit, lifecycle support, maintenance needs and current procurement terms before making a purchase or fleet decision.
參考來源
- DIY Photography via Google News - primary source
發佈時尚未取得其他官方文件。
Reboot Hub 編輯部為無人機所有者提供購買、維修、轉售及營運分析。若發現錯誤,請根據我們的編輯政策聯絡我們進行更正審查。